Home
» New Trends
»
AI Fraud Detection in Real-Time Payments: The Tradeoffs Banks Must Manage
AI Fraud Detection in Real-Time Payments: The Tradeoffs Banks Must Manage
Real-time fraud detection is not a single model that decides whether a payment is “good” or “bad.” In production, financial institutions usually combine several layers: deterministic rules, machine-learning risk scores, identity and device signals, relationship or graph analysis, network-level intelligence, and an orchestration layer that decides whether to approve, decline, hold, or step up authentication. The best design is the one that meets the institution’s loss tolerance and customer-experience goals within the time budget of the payment rail.
That tradeoff matters more as payment speed increases. An instant transfer can move before a human investigator has time to review it, so the risk decision has to happen before or during authorization. At the same time, blocking too aggressively creates false declines, customer complaints, abandoned purchases, and expensive manual reviews. AI helps widen the set of signals that can be evaluated quickly, but it does not eliminate the need for rules, human oversight, or clear risk limits.
What actually happens before a transaction is approved?
A typical real-time decision flow starts when the institution receives a transaction or payment instruction. The system enriches it with context such as account history, recent transaction velocity, device or session characteristics, merchant or beneficiary information, location, authentication events, and known relationships between entities. Rules and models then produce signals or scores. A decision engine combines those outputs with policy: low-risk activity may pass, medium-risk activity may trigger additional authentication or review, and high-risk activity may be declined or stopped when the payment scheme and applicable rules allow it.
That layered design is consistent with how major payment networks describe current fraud prevention. Visa says its fraud systems combine real-time analytics, AI-powered scoring, rules, behavioral information, and authorization controls rather than relying on one static blacklist. See Visa’s official AI fraud detection overview. Mastercard likewise describes real-time decisioning that uses transaction context, cardholder behavior, merchant relationships, graph techniques, and AI in its Decision Intelligence documentation.
Which fraud-detection approach is best for which job?
Approach
Where it is strongest
Main tradeoff
Best fit
Rules and thresholds
Known patterns, policy limits, velocity checks, blocked entities
Easy to explain but brittle when attackers change behavior
Baseline controls, instant-payment safeguards, regulatory or policy constraints
Supervised machine learning
Ranking transactions by learned fraud probability
Strong when labels are good; weaker under label delay, drift, or new attack types
Detecting unusual login, session, device, location, or interaction patterns
Useful before payment, but privacy, consent, and channel coverage must be managed
Digital banking, account takeover, high-risk sessions
Network or consortium intelligence
Seeing risk that one institution cannot observe from its own history
Broader visibility comes with external dependency, data-sharing, and integration questions
Instant payments, new beneficiaries, sparse local history
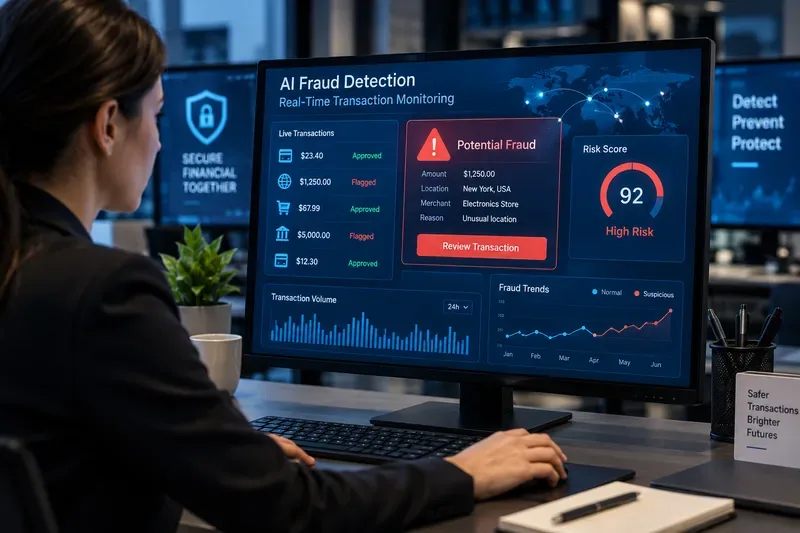
A fraud operations analyst reviews transaction signals and a high-risk alert during real-time monitoring. The screen represents a generic fraud-monitoring workflow rather than a specific bank or vendor interface.
Why are rules still necessary if AI is more adaptive?
Rules remain useful because some controls should be deterministic. If an account is on a verified deny list, if transaction velocity exceeds a defined threshold, or if policy prohibits a specific action, the institution may want a predictable outcome rather than a probabilistic score. Rules are also easier to audit and change quickly during an active fraud campaign.
The weakness is maintenance. Large rule sets can accumulate exceptions, interact in unexpected ways, and generate excessive alerts. They also tend to detect what the institution already knows. For that reason, a practical architecture usually keeps rules for hard constraints and obvious patterns while using ML to rank the ambiguous middle.
The Federal Reserve’s 2026 FedNow operating procedures illustrate this layered idea. FedNow provides participant-configurable negative lists and account activity thresholds as additional fraud-mitigation checks, while explicitly positioning them as tools that augment a participant’s own fraud practices. The current procedures are available in the FedNow Service Operating Procedures, February 2026, Version 3.5.
When does supervised machine learning become the core engine?
Supervised ML is most useful when an institution has enough representative historical transactions and reasonably reliable fraud outcomes. The model can learn combinations that are difficult to express as rules: for example, an amount that is normal for one customer but unusual for another, or a transaction that appears harmless in isolation but is risky given recent device changes and payment velocity.
The operational challenge is that fraud labels are imperfect and delayed. Chargebacks, customer reports, scam investigations, and confirmed account-takeover cases can arrive days or weeks after authorization. That means a model trained on yesterday’s labels may be learning an incomplete picture. Institutions therefore need model monitoring, back-testing, champion/challenger testing, and a defined process for responding to drift rather than assuming a model will “continuously learn” safely on its own.
Where do graph analytics and network intelligence add value?
Transaction-level models answer, “Does this payment look risky?” Graph models can ask a different question: “What is this payment connected to?” Shared devices, beneficiary accounts, phone numbers, addresses, merchants, IP ranges, or funding sources can reveal coordinated behavior that would be hard to see transaction by transaction.
This is especially useful for mule networks and organized fraud. The tradeoff is infrastructure. Graph features may require entity resolution, streaming relationship updates, and careful controls to prevent stale or weak associations from contaminating decisions. Institutions with small transaction volumes may get more value by consuming network intelligence from a payment provider than by building a large graph platform themselves.
A current example is the Federal Reserve’s FedNow Network Intelligence API, launched for early adopters on April 28, 2026. It provides sending institutions with receiver account-level data observed over the FedNow service to complement their own risk processes. The Federal Reserve describes the tool in its official Network Intelligence API announcement. The important design point is not that network data replaces local models; it adds information the sender may not otherwise have.
What about anomaly detection and behavioral analytics?
Anomaly detection is attractive because it does not require every fraud pattern to be labeled in advance. A system can compare a payment with the customer’s normal behavior, peer behavior, or a learned representation of typical activity. That can help discover new attack patterns.
The cost is precision. Unusual does not automatically mean fraudulent. A customer traveling, buying an expensive appliance, sending money to a new family member, or changing devices may look anomalous while being legitimate. Anomaly scores are therefore often most useful as one feature in an ensemble, or as a trigger for step-up authentication, rather than as the sole reason to decline a payment.
Should generative AI make approve-or-decline decisions?
Generative AI can help fraud teams summarize cases, retrieve related evidence, explain model signals in analyst-friendly language, and accelerate investigation. Some commercial fraud products are also beginning to incorporate generative techniques into decisioning; Mastercard, for example, describes generative components and graph techniques in its current Decision Intelligence Pro materials.
That does not mean a general-purpose language model should be placed directly in the critical authorization path. Payment decisions require bounded latency, stable outputs, reproducibility, security, and measurable error rates. For most institutions, the safer pattern is to use deterministic services and validated predictive models for the transaction decision, while using generative systems in analyst-assist workflows unless the generative component has been specifically engineered, tested, monitored, and governed for that use.
Why are instant payments harder to secure?
Traditional fraud operations often relied on time: a batch could be reviewed, a transfer could be held, or a suspicious item could be investigated before final settlement. Instant payments compress that window. The system must gather evidence, score risk, and apply controls fast enough that security does not defeat the purpose of real-time payment.
This makes pre-transaction checks more important. A useful stack may include beneficiary verification where available, account and device history, velocity controls, network-level signals, scam-risk indicators, and targeted customer confirmation for higher-risk transfers. The decision should be proportional: adding friction to every payment may reduce fraud but can make the service unusable.
The broader threat is also shifting. Visa’s Spring 2026 threat report said criminals were increasingly emphasizing scams and social engineering, where the victim may authorize the payment. That matters because a transaction can look technically valid even when the customer has been deceived. See Visa’s May 2026 threats report announcement.
How should different financial institutions choose a stack?
For a smaller bank or credit union
Prioritize managed risk scoring, strong rules, beneficiary and device checks, network-provided intelligence, and a small set of well-tuned review queues. Building a custom deep-learning or graph platform may not be justified if data volume and specialist staffing are limited. The key is integration quality and the ability to tune thresholds to the institution’s own customers.
For a large card issuer
Use supervised ML as a core scoring layer, enriched by network features, behavioral histories, device signals, and targeted rules. Large issuers usually have enough volume to support segmentation, challenger models, and continuous performance monitoring. The challenge shifts from “Can we build a model?” to “Can we keep false declines and model drift under control across portfolios?”
For an instant-payment provider
Emphasize pre-payment signals, velocity controls, beneficiary risk, network intelligence, and orchestration that can return a decision within strict latency limits. Graph signals are valuable when they can be computed or retrieved fast enough. Manual review should be reserved for flows that can actually tolerate a hold.
For a high-growth fintech
A hybrid vendor-plus-internal approach often gives the best speed-to-control tradeoff. External services can provide device, identity, or network intelligence while internal models capture product-specific behavior. Avoid creating a dependency on a single opaque score: retain your own policy layer, logging, and fallback logic.
How do you know whether the system is actually good?
Accuracy alone is not enough because fraud is usually rare relative to legitimate activity. A useful production scorecard should include:
Fraud capture or recall: how much confirmed fraud the system catches.
Precision: how many flagged transactions are actually fraudulent.
False-positive and false-decline rates: how often legitimate customers are disrupted.
Approval rate: whether fraud controls are suppressing good transactions.
Loss rate: fraud losses relative to transaction volume or value.
Manual-review rate and yield: how much analyst capacity is consumed and how productive those reviews are.
Decision latency: whether the system consistently stays within the payment rail’s time budget, including tail latency rather than only averages.
Calibration and stability: whether risk scores mean roughly the same thing over time and across customer segments.
Those metrics should be evaluated together. A model that catches more fraud by doubling false declines may be worse for the business. A model that improves average latency but occasionally times out during traffic spikes may be unsuitable for real-time authorization. The right operating point depends on product economics, customer expectations, payment type, and the institution’s risk appetite.
How should AI fraud systems be governed?
Fraud models affect customers directly, so governance needs to cover more than model performance. Institutions should document data sources, intended use, thresholds, overrides, monitoring, retraining triggers, security controls, and human escalation paths. Explainability requirements may differ between an analyst tool and an automated customer-facing decline, but both need traceability.
The NIST AI Risk Management Framework remains a useful cross-industry reference for managing AI risk through governance, mapping, measurement, and management. As of September 2026, NIST states that AI RMF 1.0 is being revised, so institutions should treat it as a current framework with ongoing updates rather than a frozen compliance standard.
What can AI fraud detection not solve by itself?
AI cannot turn every risky payment into a certain answer. Sparse history, first-time beneficiaries, compromised identities, synthetic accounts, delayed labels, adversarial behavior, and legitimate-but-unusual customer activity all create ambiguity. Authorized scams are particularly difficult because the customer may pass authentication and intentionally submit the payment after being manipulated.
That is why strong fraud prevention is a system, not a model. The most resilient approach combines fast predictive scoring with deterministic controls, network context, authentication, customer communication, post-transaction investigation, and feedback loops. The goal is not to maximize the number of blocked transactions. It is to reduce fraud losses while preserving legitimate payment flow and keeping every automated decision within an explainable, monitored risk process.
Bottom line
There is no universally best AI fraud-detection architecture. Rules are best for hard constraints and known patterns. Supervised ML is strongest when high-quality labels and volume exist. Anomaly detection helps surface unfamiliar behavior but needs guardrails. Graph analytics are valuable for connected fraud rings. Behavioral and device signals improve context around account takeover. Network intelligence fills gaps that a single institution cannot see.
For most financial institutions, the practical recommendation is a layered stack with a policy-controlled decision engine at the center. Measure fraud capture, false declines, approval rates, losses, review burden, and latency together. Add more complex AI only when it produces a measurable improvement under those constraints. That is how real-time fraud detection becomes a dependable control rather than just a sophisticated score.